
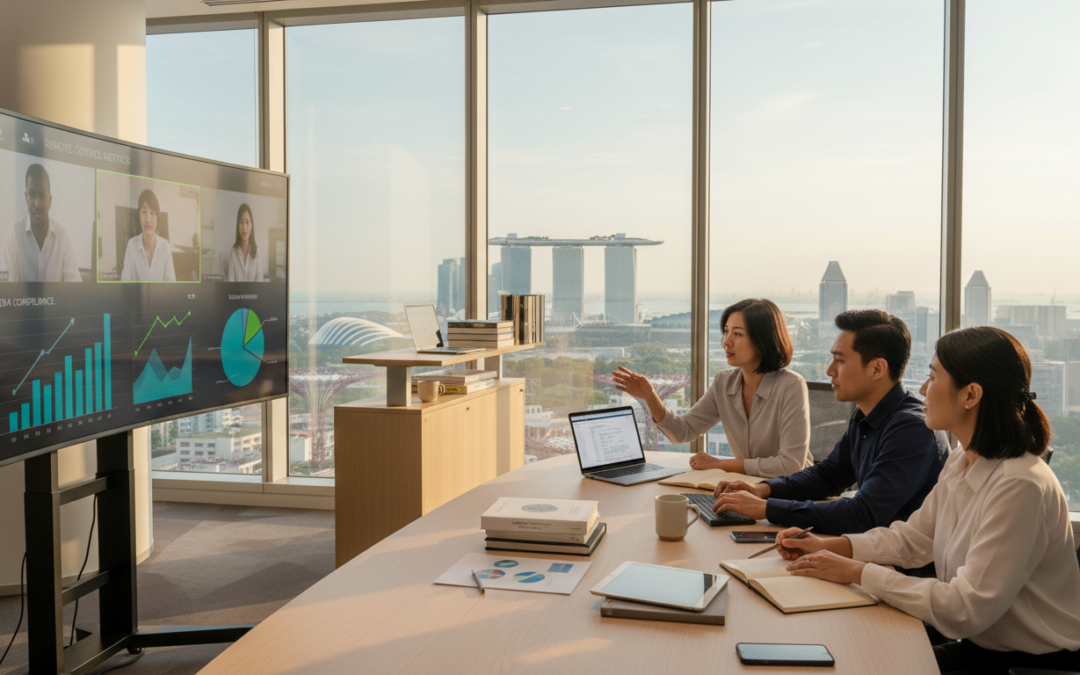
Can oversight keep pace with teams that work apart and across sites?
This guide answers that question for governance, risk and compliance leaders today.
We define what remote internal controls mean in a local context and set practical expectations. The aim is clear: keep authorisation, accuracy and audit evidence reliable even when people execute processes off-site.
You will find step‑by‑step solutions for choosing the right delivery type — fully off-site, on‑site or hybrid — based on process complexity and security needs. The guide links control design to remote audits so leaders can select tools that protect data, reduce fraud risk and preserve retrievable evidence.
We preview why this matters in the present world, how to implement a robust framework, and how to run professional testing and audits. Use this guide if you are in finance, IT, operations, risk or audit and want repeatable, measurable results for the future.
Key Takeaways
- Understand the definition and purpose of remote internal controls.
- Choose a delivery type that fits process risk and security needs.
- Design controls to protect data and maintain clear audit evidence.
- Adopt tools and workflows that support measurable control performance.
- This guide suits finance, operations, IT, risk and audit owners seeking practical solutions.
Why remote internal controls matter for Singapore organisations today
The shift to distributed workforces has altered how risk and oversight should be applied across teams.
How hybrid work changes risk, accountability and oversight
Supervision becomes less visible and approvals can turn informal. Managers may see results but not the steps taken, so evidence trails and system logs are essential.
New risks include heavier reliance on digital channels, more endpoints accessing systems and greater exposure to data leakage through insecure file handling.
Operational resilience and continuity expectations
MAS and ABS encourage firms to remain vigilant and adopt sound practices across operations, technology and information security.
Operational resilience means controls must keep working under split teams, limited office access or severe disruption. Regular internal drills and industry exercises show whether continuity plans hold up under pressure.
- Risk areas: operations, technology and information security, fraud and staff misconduct, legal and regulatory risk.
- People and culture: weaker coaching and tone-from-the-top can erode compliance unless actively reinforced.
Resilient arrangements protect service continuity, guard customer trust and help firms meet regulatory expectations now and into the future.
remote internal controls singapore business best practices for governance, risk, and compliance
Prioritise a risk-led approach so teams can protect critical workflows and maintain credible audit trails.
Start with a risk assessment across operations, technology, and information security
Identify critical processes, map system touchpoints and note where working off-site creates new failure points. Run a checklist per function (finance, procurement, HR, IT) and include legal and regulatory checks.
Design controls to reduce fraud and staff misconduct
Strengthen pre-approval rules, enforce independent review and add exception reporting. Stop reliance on informal messaging for approvals; require evidence that supports every audit trace.
Clarify roles, segregation of duties and delegated authority
Define owners, reviewers, backups and approvers. Document thresholds to avoid rubber‑stamping under time pressure and keep current role lists for management review.
Set secure access and standardise evidence trails
- Access: apply least privilege, MFA and timely joiner‑mover‑leaver steps.
- Documentation: use consistent naming, process narratives and defined evidence retention.
Testing, monitoring and people
Combine periodic control testing with continuous metrics (overdue approvals, privileged access changes). Run internal drills to simulate outages and key person absence.
Start with quick wins — access hardening and evidence standards — then move to automation and analytics for lasting success. See our terms and conditions for governance references.
Tools and operating model for remote control testing and remote audits
An effective audit programme pairs the right technology with clear roles and repeatable rhythms. Start by matching process complexity and evidence sensitivity to the chosen delivery mode. This decision affects data handling, accreditation needs and the number of participants you can include.
Choosing a delivery mode
Use off‑the‑shelf collaboration tools for straightforward processes and walkthroughs. These setups work well for interviews, screen shares and light evidence capture using familiar apps and standard devices.
For higher-risk or complex areas, justify a dedicated platform with secure bilateral links, annotation, geo‑tagging and optional assistive wearables. Such solutions reduce exposure when evidence sensitivity or regulator expectations are high.
Planning with security and evidence in mind
Plan access provisioning, secure file transfer and controlled virtual rooms. Define rules for recordings, screenshots and redaction before fieldwork starts.
Define what counts as sufficient appropriate evidence: validated system reports, correlated logs and signed approvals. These steps preserve integrity and reduce fraud risk.
Operating model and documentation
Assign owners, independent testers and reviewers, and publish escalation paths. Schedule quarterly testing cycles, continuous monitoring for key risks, and regular tool refreshes.
- Metrics to track: timeliness, exception rates, override frequency, access changes and remediation ageing.
- Keep documentation audit‑ready: maintain narratives, risk and control matrices and flowcharts with version control aligned to actual execution.
Practical support is available for teams that need virtual audit services — see EY’s virtual audit services — and consider hybrid meeting setups for evidence review using a managed meeting-room support. These steps help sustain reliable audits while protecting security and data integrity.
Conclusion
Leaders should close the loop by confirming ownership, evidence and reporting pathways. Make decisions today that convert policy into repeatable practice. Ensure each team knows who owns key checks and how to produce audit‑ready records.
Keep risk assessment, anti‑fraud design and clear delegated authority at the core. Harden access and standardise evidence so reviewers can validate activity without delay. Maintain a steady cadence of testing, monitoring and internal drills to show resilience.
Action checklist for management: confirm ownership, confirm evidence standards, confirm access governance, confirm reporting and remediation, and confirm training for people and teams. Use audit methods that match process complexity and keep documentation current to support future audits and industry expectations.
FAQ
What are the key risks that arise from remote and hybrid working arrangements?
How should organisations assess risk across operations, technology and information?
What design changes reduce fraud and staff misconduct in distributed teams?
How do I clarify roles and delegated authority for remote teams?
What are best practices for secure access to systems and sensitive documents?
How should organisations standardise process documentation for remote execution?
What monitoring cadence works for testing remote controls?
How do you build a people‑and‑culture layer that supports compliance remotely?
What tools suit remote audit delivery: collaboration apps or dedicated platforms?
How do you plan remote audits while protecting information security?
How should the control function be structured for effective remote testing?
What documentation keeps controls audit‑ready in a distributed environment?
How often should access rights and control effectiveness be reviewed?
How can small organisations implement these practices without large teams?
What metrics demonstrate success for a governance, risk and compliance programme?

Dean Cheong, CEO of VOffice, is a Singapore-based specialist in scaling B2B businesses. His work centers on optimizing sales operations, launching effective go-to-market strategies, and leveraging CRM tools to drive consistent revenue expansion. With a foundation in business banking and finance from Nanyang Technological University, Dean brings both strategic insight and real-world execution to every engagement.