
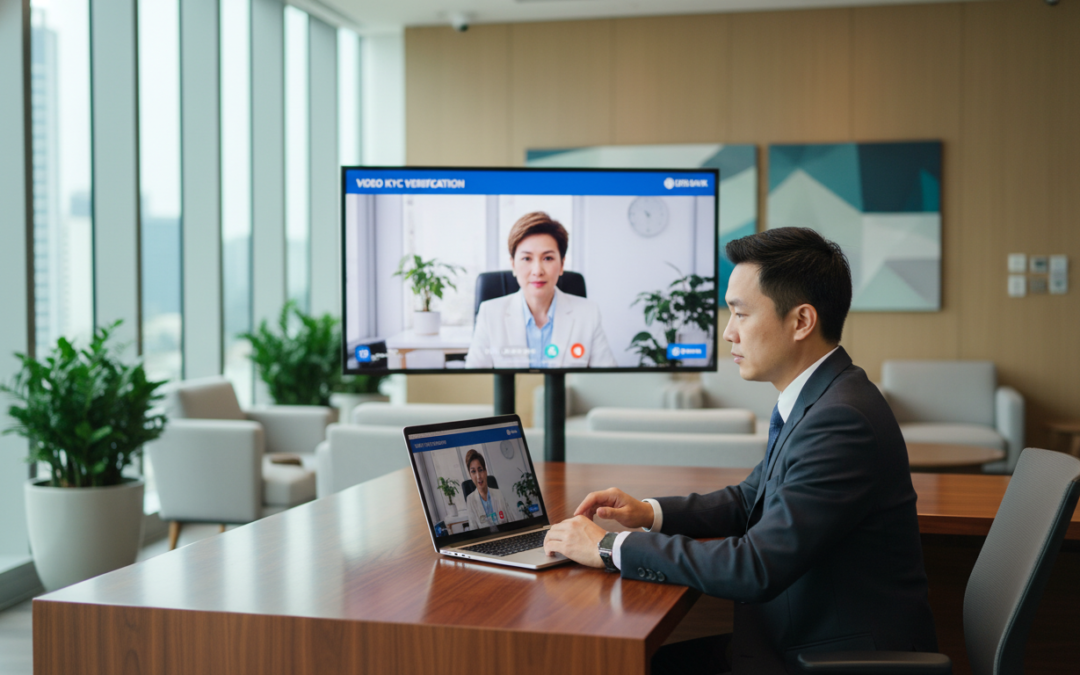
Could remote identity checks replace in-person account openings without weakening controls?
This guide defines what an attended, live verification session means for corporate onboarding and who should use it: incumbent banks, digital banks and fintech providers operating in Singapore that need audit‑ready remote onboarding.
The Monetary Authority expanded approved options in 2019 to include live checks and third‑party providers. Its approach is technology‑neutral and risk‑based, aligned with FATF principles.
Expect remote verification to be triggered by risk — for non‑resident directors or higher‑value accounts — rather than applied to every applicant. When used well, it reduces drop‑offs, delivers stronger compliance evidence, and models attended verification to approximate in‑person checks.
Preview: the article will cover regulatory expectations, scope and triggers, journey design, KYB/UBO checks, document and data handling, implementation steps, vendor selection, fraud controls and audit‑ready governance. The aim is a clear, defensible process that complements existing eKYC tooling.
Key Takeaways
- Live attended checks support remote corporate onboarding while preserving controls.
- Regulators prioritise controls and evidence over a single technology choice.
- Use risk triggers to decide when to apply remote verification to accounts.
- Proper design reduces customer drop‑off and strengthens compliance records.
- This guide helps banks and fintechs build an audit‑ready operating model.
Why video KYC matters for Singapore business banking onboarding today
Faster, defensible verification protects customers and the institution.
Remote live sessions let reviewers confirm a corporate applicant’s presence and intent in one recorded interaction. This reduces long follow-up cycles and repeated document requests that drive abandonment, especially for cross-border applicants who cannot travel.
Reducing abandonment while keeping assurance defensible in audits
Good customer experience only helps if records hold up under scrutiny. Recorded sessions consolidate consent, live presence and document authenticity into a single, traceable file for regulatory inspection.
Supporting remote account opening and cross-border growth
These checks let banks acquire customers in markets where branch visits are impractical. That supports expansion without redesigning onboarding per jurisdiction.
Where attended review sits alongside document-only and in-person checks
Document capture stays efficient for low-risk cases. Attended review is reserved for higher risk, inconclusive automated outcomes or complex ownership structures.
| Method | Best for | Evidence |
|---|---|---|
| Document-only | Low-risk accounts | Uploaded files, system logs |
| Attended live review | Non-resident or higher-risk applicants | Recordings, screenshots, session logs |
| In-person | Traditional profiles or special requirements | Signed forms, branch records |
Regulatory landscape in Singapore: MAS expectations, FATF principles and PSA considerations
Regulators expect remote identification to meet the same evidential standards as face‑to‑face checks.
MAS and ACRA set the baseline for regulations and compliance expectations. Singapore aligns closely with FATF, meeting or exceeding most benchmarks, and since 2019 has approved attended remote verification and third‑party reviewers where controls are adequate.
Technology‑neutral, risk‑based customer due diligence and accountability
MAS evaluates outcomes, not specific tools. Put simply, the authority cares that controls and evidence deliver equivalent assurance.
- Translate technology‑neutrality: document how tools produce the same level of proof as in‑person checks.
- Risk‑based control: trigger attended checks where automated screening is inconclusive or risk is elevated.
- Accountability: assign reviewer ownership, escalation paths and clear decision logs.
Payment Services Act coverage and when additional licensing checks apply
The PSA covers issuance of accounts, cross‑border transfers, e‑money, merchant acquiring, money‑changing and digital token services.
If an institution or affiliated fintech offers regulated services, onboarding must include licensing verification and activity checks tied to those services.
Penalties and supervisory scrutiny for KYC and AML non‑compliance
Enforcement is material. Financial institutions can face fines up to S$1 million per offence, with daily fines of S$100,000 for repeated breaches.
Individuals convicted of money laundering face fines up to S$500,000 and/or seven years’ imprisonment. That risk underlines why written policies on evidence retention, data handling and reviewer training are essential for defensible compliance.
Define scope, risk appetite and triggers for attended video verification
Set clear scope and trigger rules to ensure attended checks are applied where they matter most.
Decide which products and segments use attended review. Focus on corporate current accounts, multi‑currency accounts and merchant accounts where remote review replaces branch interviews. Prioritise use for cross‑border customers and where branch access is limited.
Which customer types to prioritise
Give priority to non‑resident directors, foreign‑owned companies and complex structures with multiple shareholders across jurisdictions. These profiles raise higher risk and often need live confirmation of presence and intent.
Align triggers with AML scoring and transaction expectations
Use AML scores and expected transactions — volume, frequency, corridors and counterparties — to decide when document‑only checks are insufficient. Specify that high initial funding, unusual corridors or opaque business activity escalate the case to an attended session.
- Scope decision: list covered products and segments that require live review.
- Operational risk appetite: define “high risk” by industry, geography, funding size and ownership chains.
- Ownership complexity: multiple owners, beneficial owners or cross‑jurisdiction directors trigger attended checks.
- Exceptions and governance: set rules for automated failures, altered documents or vague activity; record who activates or overrides a trigger and why.
Document these requirements in plain operational terms and link policy to your reviewer guidance and terms and conditions so decisions stay audit‑ready.
Design the target video KYC journey for corporate and KYB onboarding
A clear, concise onboarding path turns a single live session into a complete, audit-ready verification interaction.
Start with explicit consent. Capture the customer’s agreement to the live session and to process personal data. The notice must state recording, retention period and the purpose in plain language.
Attended live session: identity, intent and presence
Structure the call so the reviewer confirms who the applicant is, why they seek the account, and that they act voluntarily.
Use a short script for consistent questions and to reduce follow-ups. Trained reviewers should log decisions in real time.
Integrated document authenticity checks
While on the call, validate IDs and corporate papers. Check consistency between documents and spoken information.
Confirm the applicant can control submitted documents (showing originals, opening files) to prove possession.
Evidence capture and structured records
Record the session, take screenshots at key moments (ID display, face match) and retain session logs with timestamps and reviewer ID.
Store a concise decision note that links to the recording and to the documents reviewed for audit purposes.
Fallbacks and escalation
If connection or image quality fails, allow a re-attempt or route to an alternative verification channel. For unresolved doubts, require in-person review.
Escalate on suspicion: inconsistent answers, document mismatches or signs of coercion must trigger enhanced review and a senior reviewer.
| Step | What to capture | Escalation trigger |
|---|---|---|
| Consent | Explicit consent record, data notice | Refusal to consent |
| Live session | Recording, reviewer ID, Q&A log | Poor image, evasive answers |
| Document checks | Screenshots, file hashes, cross-check notes | Mismatch with claimed identity |
| Decision | Structured note, retention link to records | Unresolved risk → in-person or enhanced due diligence |
KYB essentials: verifying companies, directors and ultimate beneficial owners
A clear KYB process begins by proving the company’s existence, then mapping who truly owns and manages it.
Define scope first. Verify the company record, then confirm directors, authorised signatories and shareholders. Finally, identify ultimate beneficial owners and document their control and benefit paths.
Identifying key people
Map shareholdings and control lines. Use registry extracts, shareholder registers and corporate minutes to support ownership chains.
Handling multi‑jurisdiction stakeholders
Standardise required evidence so overseas owners submit consistent documents. Schedule separate attended sessions for remote directors or owners to avoid time‑zone delays and repeated follow‑ups.
Enhanced diligence for higher risk cases
Apply enhanced due diligence for foreign‑owned structures, unusual transaction corridors or unclear activity descriptions. Require source of wealth and funds, and link outcomes to account controls — staged access, lower limits or restrictions until verification is complete.
- Operational ownership: assign a team for KYB decisions and record exceptions for audit.
- Practical ID: ensure every owner is supported by credible documents and a traceable decision log.
Data and document requirements to support defensible due diligence
A clear document set turns onboarding from guesswork into a defensible decision for auditors and reviewers.
Core company documents should be current and consistent. Provide a recent ACRA Business Profile extract, the Company Constitution, registers of directors and shareholders, and a Board Resolution authorising account opening.
Identity and address proof for individuals
Directors, signatories and UBOs must submit passport copies and recent proof of residential address (utility bill or bank statement within three months). Include visa or entry pass details when relevant.
Operational substance, activity and transactions
Prepare a concise description of business activities, a one‑page summary of how money flows, and website or client contracts where available. State expected currencies, monthly volumes and key countries for transactions.
Source of funds and initial funding
For initial deposit and ongoing funding, supply bank statements, investment agreements, parent company resolutions or loan documents. Clear proof here reduces follow-up queries and supports due diligence.
- Checklist: ACRA extract, constitution, registers, board resolution.
- Director ID and address proof; visa details if applicable.
- Operating address evidence — leases or utility bills; virtual office proof may trigger enhanced review. See virtual office guidance.
Remember: the aim is coherent, verifiable information that supports a timely account opening decision and audit-ready compliance.
video kyc singapore business bank: implementation steps from pilot to production
Begin with a narrow pilot that targets a high-impact customer segment to validate controls and evidence capture.
Start small and scale. Run a pilot for non-resident corporate applicants to test the process, reviewer scripts and technical integrations. Use results to refine operations before full roll‑out.
Mapping the end-to-end process across channels, teams and systems
Map intake, document upload, risk scoring, session scheduling, reviewer decisioning and account activation. Keep each step auditable and link records to the reviewer note.
Integrating onboarding with AML screening, sanctions checks and ongoing monitoring
Connect onboarding outcomes to AML and sanctions checks so hits trigger case management. Implement watchlist monitoring and log alerts against account records for early review.
Setting service levels and realistic timelines for corporate account opening
Set service targets that mirror reality: traditional banks often take 4–8 weeks end‑to‑end, with complex cases longer. Offer a fast lane for complete, low‑risk submissions.
| Stage | Owner | Service level |
|---|---|---|
| Pilot | Onboarding team | 4 weeks |
| Full screening & checks | Compliance / AML | 2–6 weeks |
| Activation & early monitoring | Operations / RM | 3–6 months staged limits |
| Audit retrieval | Records / IT | < 24 hours |
Operational controls: assign clear handoffs, own exceptions, and apply staged access for new accounts. Track metrics such as abandonment rate, time to decision and QA pass rates to measure success.
Choose the right technology and vendor model for video KYC services
Picking a model early shapes control, speed and how evidence is stored for regulatory review.
In-house reviewers give institutions tighter control over decisions and training. They simplify accountability and make QA direct.
Third‑party services provide scale and extended hours across time zones. Many banks use them when internal capacity cannot support high volumes.
Operational implications and risk controls
Keep decision ownership even when you outsource execution. Contract clear SLAs, QA obligations and audit access so the bank can defend decisions.
Key selection criteria
- Coverage: choose solutions that support the jurisdictions your company and directors come from to avoid gaps.
- Biometric security: require liveness checks, face match and anti‑spoofing to reduce identity fraud.
- Scalability & deployment: the platform should run assisted, hybrid and automated flows without heavy rebuilds.
- Integration: vendor tooling must tie into onboarding, case management and screening so documents and decisions are searchable.
Data protection and retention
Define where recordings and records are stored, who can access them and how tamper‑resistance is implemented.
Match retention policies to regulations and internal compliance requirements. Keep a clear map of access rights and deletion routines.
| Model | Strength | Key risk control |
|---|---|---|
| In‑house reviewers | Tight control, direct training | Clear escalation, dedicated QA team |
| Third‑party services | Scalable coverage, time‑zone reach | SLAs, audit access, decision ownership retained |
| Hybrid | Flexible deployment, cost balance | Integrated workflows, shared QA metrics |
Fraud and security controls for remote identity threats
Fraudsters now target corporate onboarding with sophisticated identity manipulation techniques. Remote processes are attractive because static documents can be copied, altered or reused. That raises the threat for corporate account openings and for institutions that rely on non‑face‑to‑face flows.
Preventing impersonation, synthetic identity and deepfake-based attacks
Threat model: attackers blend stolen paperwork, synthetic identity data and realistic deepfakes to bypass document-only checks. These methods aim to impersonate directors or owners and to mask true control.
Layered assurance: liveness, behavioural cues and contextual questioning
Attended sessions increase defence by testing presence and responsiveness in real time. Practical steps include liveness prompts, face-to-ID comparison and short contextual questions that genuine directors can answer consistently.
- Watch for coached or scripted replies and signs of reluctance or off-screen prompting.
- Record key checks, note the rationale for pass/fail decisions and retain timestamps for audit review.
- Step-up controls: add extra screening, second‑reviewer approval or enhanced due diligence when red flags appear.
Embed fraud controls into the onboarding workflow so reviewer decisions, escalation routes and evidence stay linked. That approach preserves compliance and strengthens proof when regulators or auditors request information.
Governance, training and record-keeping for audit-ready compliance
A well‑documented QA regime ensures reviewers apply rules consistently and explains exceptions.
Reviewer standards: define training modules that cover how to run attended sessions, spot red flags, handle multi‑person KYB scenarios and use consistent questioning. Include practical roleplays, checklists and quarterly refreshers so new rules reach front‑line staff quickly.
Quality assurance and decision ownership: build a QA framework with sampling, second‑line review and calibration sessions. Record who approved each outcome and why, linking the decision to the exact evidence and policy clause. Even when an external provider supports execution, the institution must retain outcome ownership.
Tamper‑proof records and traceability: store immutable logs and secure recordings with timestamps, reviewer IDs and file hashes. Ensure rapid retrieval for regulators and auditors, and map traceability from original application to the final decision note.
Retention, access and post‑activation monitoring: set retention schedules that meet regulations and internal requirements. Limit access by role and enforce encryption and audit trails. Apply staged access for new accounts: screening and behavioural monitoring are heightened for the first 3–6 months, with limits lifted only after due diligence and activity match expectations. For further AML guidance see AML guidance.
Conclusion
A practical rollout treats attended verification as a targeted step‑up, not a universal replacement. Use it where risk scores, ownership complexity or cross‑border factors make document-only checks insufficient. This guide shows how to make that choice.
Make the programme defensible. Define clear triggers, require KYB coverage for directors and owners, list required documents and keep audit‑ready records with tamper‑proof links to each decision.
Operational readiness matters. Train reviewers, run QA sampling and integrate screening so risk is managed after account activation.
Remember registration realities: a valid UEN, CorpPass or MyInfo Business flow speeds processing and avoids delays for company registration and initial deposit checks.
Next steps: confirm scope and appetite, pilot a targeted segment, validate governance, then scale. Digital-first fintech can extend reach while meeting compliance expectations.
FAQ
What is the purpose of implementing attended video verification for corporate account opening?
Which types of corporate customers should be prioritised for live verification?
How does a live session fit with document-only electronic checks and face‑to‑face verification?
What regulatory expectations should institutions follow when using remote verification?
What core corporate documents are typically required to support defensible due diligence?
How should banks verify ultimate beneficial owners and shareholders in multi‑jurisdiction structures?
What evidence should be captured during an attended verification session?
How do institutions handle inconclusive checks or suspected fraud during a session?
What technical controls reduce impersonation and deepfake risks in live sessions?
Should banks build an in‑house verification team or use third‑party reviewers?
How should an institution integrate remote onboarding with AML screening and ongoing monitoring?
What are realistic service levels and timelines for corporate account opening with attended verification?
What data protection and retention controls are required for recorded sessions and documents?
What training and governance measures ensure audit‑ready decisioning?
When is enhanced due diligence required for foreign‑owned or high‑risk activities?

Dean Cheong, CEO of VOffice, is a Singapore-based specialist in scaling B2B businesses. His work centers on optimizing sales operations, launching effective go-to-market strategies, and leveraging CRM tools to drive consistent revenue expansion. With a foundation in business banking and finance from Nanyang Technological University, Dean brings both strategic insight and real-world execution to every engagement.